Table of contents
Managing Google reviews in compliance with the GDPR can seem complex, but it is a crucial issue for protecting your customers' privacy. Discover 5 practical methods for collecting and using these reviews while scrupulously respecting the regulation. You'll find advice on choosing the right legal bases, securing information and ensuring complete transparency toward your customers.
The number of review requests and platforms tracked depends on the plan, enough to choose your subscription plan to suit your business.
Essential GDPR principles for customer reviews
Review collection always takes place after the purpose of processing has been precisely determined. We clearly identify the appropriate legal basis for each operation: order tracking, review request, publication or marketing use. This approach strengthens personal data protection and guarantees our GDPR compliance at every step. This aspect connects with our guides on the legal framework for reviews.
Legal bases and customer consent under the GDPR
To publish a review, consent is generally the most suitable legal basis. We make sure it is given freely, specifically and unambiguously, and no pre-ticked boxes are used. GDPR for customer reviews requires these precautions to effectively protect each user's data.
- Absolute traceability: We systematically record the timestamp, IP address, exact content and session ID to prove consent in the event of an inspection by the CNIL.
- Separate choices: Our forms clearly separate the review request, the newsletter subscription and sharing with third parties to meet granularity requirements.
- Easy right to withdraw: All our emails include a visible unsubscribe link, and a dedicated space lets people change their preferences at any time.
Some operations, such as order tracking, can rely on legitimate interest, but publishing reviews always requires explicit consent. We systematically document our impact assessment and offer a clear opt-out in all our communications.
Data minimization, retention and security under the GDPR
We only collect the personal data that is strictly necessary: a username, the rating, the comment and the order number. The email is used to verify the purchase but is never displayed publicly. Each use is covered by specific consent to prevent any diversion from the original purpose of processing.
Precise retention periods are applied automatically: identifiers are kept for between 1 and 3 years depending on their use, then anonymized or deleted. This storage limitation meets the GDPR's requirements while preserving the value of testimonials for our community. These rules come on top of the legal obligations governing review publication.
Transparency and customer rights under the GDPR
When collecting data, a clear information notice is provided. It states the data controller, its purposes, the retention periods and the contact details of our DPO so you can exercise your rights. This transparency is essential to building trust and demonstrating our commitment.
Our public moderation policy sets out objective grounds for rejection (defamatory content, sensitive data or spam). In case of rejection, the author receives a detailed explanation within set deadlines, which further supports GDPR compliance.
Data security is an absolute priority: all exchanges and storage are encrypted, access is restricted to what is strictly necessary, and administration is protected by two-factor authentication. Detailed activity logs document every operation to guarantee traceability.
GDPR-compliant customer review forms and moderation
Our forms follow privacy by design: every field is justified, the full name is optional and no box is pre-selected. This approach ensures immediate GDPR compliance from the very first interaction with our customers.
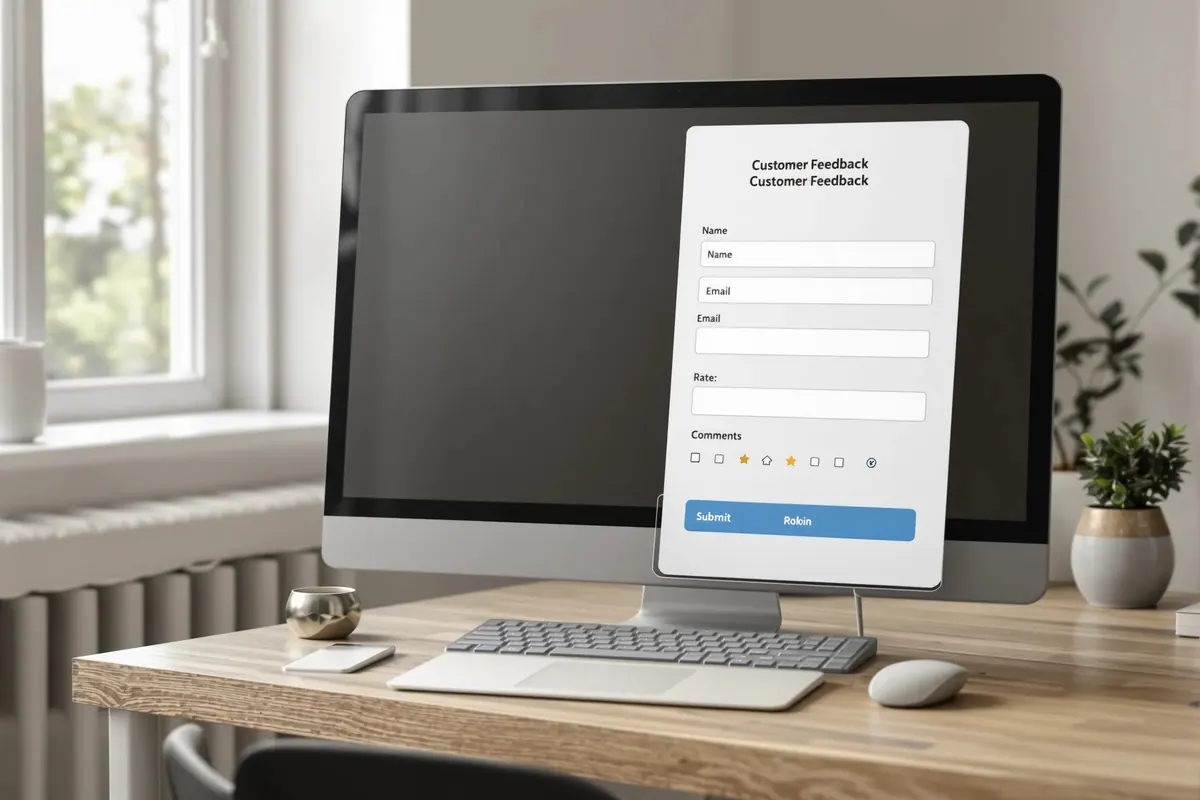
Designing a GDPR-compliant customer form
Our GDPR consent form collects only the essentials: username, rating, comment and an empty consent box. The "Publish my full name" option is turned off to respect the confidentiality each customer wants.
Every form offers direct access to our privacy policy and our moderation charter. After a purchase, we send a unique link tied to an internal ID to show the "Verified purchase" badge, without revealing the email, which guarantees data security and the authenticity of online reviews. Read our guide to discover our CRM integration and smart automation solutions. This badge also reinforces Google review authenticity in users' eyes.
Transparent moderation and anti-fraud measures under the GDPR
Our moderation process follows defined deadlines and applies documented, objective criteria. We record each step with a timestamp to ensure GDPR compliance and maintain complete traceability. GDPR customer files, stored separately from public reviews, are accessible only to authorized staff.
Our system automatically detects anomalies: repeated attempts, suspicious IP addresses or text similarities. These submissions are suspended and then reviewed manually, combining technology and human expertise to protect the integrity of customer reviews. If a fake review still targets your profile, here is how to report a fake Google review.
GDPR-compliant reuse and cookies
Before any commercial use of a review, we obtain specific, documented consent. Without permission, we systematically anonymize the testimonial (e.g. "Paul L.") and blur images, thereby respecting individuals' rights while still showcasing their feedback. This requirement for sincerity also rules out paid or fabricated reviews, which carry heavy consequences for a business.
Our Google reviews widgets and analytics tools only activate once cookie consent has been obtained. Our banner specifies each use and the retention period, and allows detailed management of preferences to ensure compliance with the European Union's e-privacy regulations.
GDPR-compliant emails and customer files
Our email and SMS exchanges scrupulously respect the obligations of the GDPR and personal data protection regulations. Every message systematically contains the required legal notices and an immediate unsubscribe option, ensuring a transparent, trustworthy customer relationship. These obligations are part of the French legal framework for online reviews, which goes beyond the GDPR alone.
GDPR rules for customer emails and SMS
For post-purchase emails asking for a Google review, we rely on legitimate interest as the legal basis. This approach is valid as long as a visible unsubscribe link is included and a documented impact assessment (LIA) is kept. Processing personal data by email (GDPR email personal data) demands absolute transparency to avoid any use of data that wouldn't match customers' reasonable expectations.
For promotional SMS, we always collect prior, explicit consent. Each message clearly states the sender's identity and the precise purpose of the communication, and includes a STOP option so recipients can easily withdraw their consent at any time.
- Explicit subject line: our emails use a clear subject indicating that it's a review request tied to a recent purchase, with no commercial ambiguity.
- Complete GDPR information: each message summarizes the essentials (data controller, purpose, retention period, rights) and links to our detailed privacy policy and to the preference management center.
- Secure proof of purchase: we link each request to an order number so that a "Verified review" badge can be displayed, while protecting sensitive information.
Our review management system physically separates customer identifiers from published content. This architecture limits data use to what is strictly necessary, simplifies review management and minimizes the risk of information leaks during everyday operations.
Email example and data portability under the GDPR
Here is an example of a fully compliant GDPR email: "Hello [First name], thank you for your order of [date]. Your opinion matters! Purpose: improving our services through the collection of verified reviews. Controller: Plus Avis Client. Retention: 2 years. Exercise your rights: [link]. Unsubscribe: [link]." This format meets all the transparency obligations imposed by the GDPR.
We make personal data portability easy through simple exports in CSV or JSON format. Through their "My reviews" area, customers can download all of their information, timestamped and electronically signed, keeping full control over their data.
| Channel | Legal basis | Main obligations |
| B2C email | Legitimate interest or consent | Unsubscribe option, impact assessment, explicit purpose |
| Marketing SMS | Express consent | Prior authorization, working STOP, clear identification |
| Public widgets | Cookie consent | Manual activation, detailed purposes, custom settings |
Tools and international transfers under the GDPR
We favor solutions hosted within the European Union to maximize the legal security of personal data. When international transfers are unavoidable, we apply the EU's Standard Contractual Clauses, combined with advanced encryption whose keys are managed independently.
All our subprocessors sign a strict data processing agreement (DPA) specifying the purposes, the technical and organizational security measures, server locations and erasure procedures. Read our comparative analysis of automated, GDPR-compliant customer review platforms to learn about the guarantees offered by each solution, strengthen customer trust, optimize review collection and make sure data use fully complies with the regulation.
Frequently asked questions
What are the 7 key GDPR principles applied to customer reviews?
The GDPR rests on seven fundamental principles to ensure personal data protection. These principles govern the use of customer reviews while guaranteeing transparency:
- Lawfulness: every processing activity requires valid legal bases such as explicit consent
- Purpose limitation: review collection stays separate from other uses such as marketing
- Data minimization: only collect the information that is strictly necessary
- Accuracy: customers can correct their reviews if needed
- Storage limitation: a defined, justified retention period
- Integrity and confidentiality: securing data against unauthorized access
- Accountability: complete documentation to prove compliance
We rigorously apply these principles at every stage of review management.
What GDPR rights do your customers have regarding their reviews?
Customers have essential rights regarding their Google reviews and other ratings:
- Right of access: view all the information concerning them
- Right to rectification: edit a published review if necessary
- Right to erasure: request deletion of all or part of their data
- Right to restriction: temporarily block the publication of a review
- Right to data portability: export their reviews in a reusable format
- Right to object: refuse further use for other purposes
To ensure compliance, we offer a simple, secure procedure: requests are verified through an order ID and handled within 30 days at most. Every action is rigorously logged to respect individuals' rights.
Are Google reviews considered personal data under the GDPR?
Absolutely. Any Google review containing identifying elements (last name, first name, photo, identifiable username) is personal data protected by the GDPR. Even a combination of pieces of information can make it possible to identify a person indirectly.
We pay particular attention to:
- Obtaining clear consent before publication
- Guaranteeing full transparency about how data is used
- Ensuring confidentiality through appropriate technical measures
- Offering anonymization on simple request
The penalties for non-compliance are severe (up to €20M or 4% of annual turnover). That is why our review collection system builds in personal data protection by design. Preserving users' rights is at the heart of our review management.